
 Key Takeaways
- Compliance with global OEM standards: Aligning operational workflows with VGP requirements (confidentiality, TISAX guidelines).
- Security-first culture: Introducing Clean Desk, Clean Screen, and mandatory workstation locking (Win+L).
- Airtight vendor management: Restricting data processing to the EEA and mandating Data Processing Agreements (DPAs) for every linguist.
- Infrastructure integration: Deploying secure Phrase/Memsource environments and encrypted data transmission channels.
- Result: Successfully passing vendor security assessments and securing multi-year contracts for critical automotive projects.
Challenge: A passport to the Automotive sector
Entering a partnership with Volkswagen Group Polska (VGP) poses a major operational test for any language service provider. Global automotive players place data security on par with service quality. My mission was to architect a security ecosystem that safeguards trade secrets — ranging from strategic investment plans to confidential prototype technical documentation.
The core challenge lay in the nature of the translation industry: relying on distributed resources and external freelance partners. I needed to establish a framework in which every stakeholder in the supply chain — from translators to desktop publishers — operated under a strictly defined security regime without compromising productivity.
Implementation: Living process documentation
Central to the implementation was ensuring full accountability through systematic Records of Processing Activities (ROPA) and routine internal audits to identify and mitigate IT infrastructure vulnerabilities early.
In close collaboration with our legal counsel, I drafted the core framework: the Information Security Policy (ISP) and Data Protection Policy. These were far from shelfware; they drove tangible changes in daily operational hygiene:
- Physical security: Enforcing paper destruction standards (DIN 66399 P-4 shredding), locking server racks, securing sensitive hardcopy files in restricted areas, and instituting strict Clean Desk and Clean Screen rules.
- Sub-processor control: Drafting custom Data Processing Agreements (DPAs) that strictly prohibit data processing outside the European Economic Area (EEA).
- IT Infrastructure: Mandating all translation work within the Phrase (formerly Memsource) cloud environment to restrict local Translation Memory downloads, alongside encrypted transmission channels (VPN/SFTP).
- Security Awareness: Conducting mandatory security training for staff and contractors, culminating in formal non-disclosure and compliance acknowledgments.
- Rack NAS Deployment: To meet strict client specs, we upgraded our hardware stack with a QNAP rack-mounted NAS dedicated to encrypted file hosting, automated backups, and system snapshots.
- Fibre & Site-to-Site VPN: To handle high-bandwidth data transfers between clients and our Poznań and Wrocław offices, we upgraded to 1 Gbps fiber internet, linked securely via a site-to-site VPN tunnel.
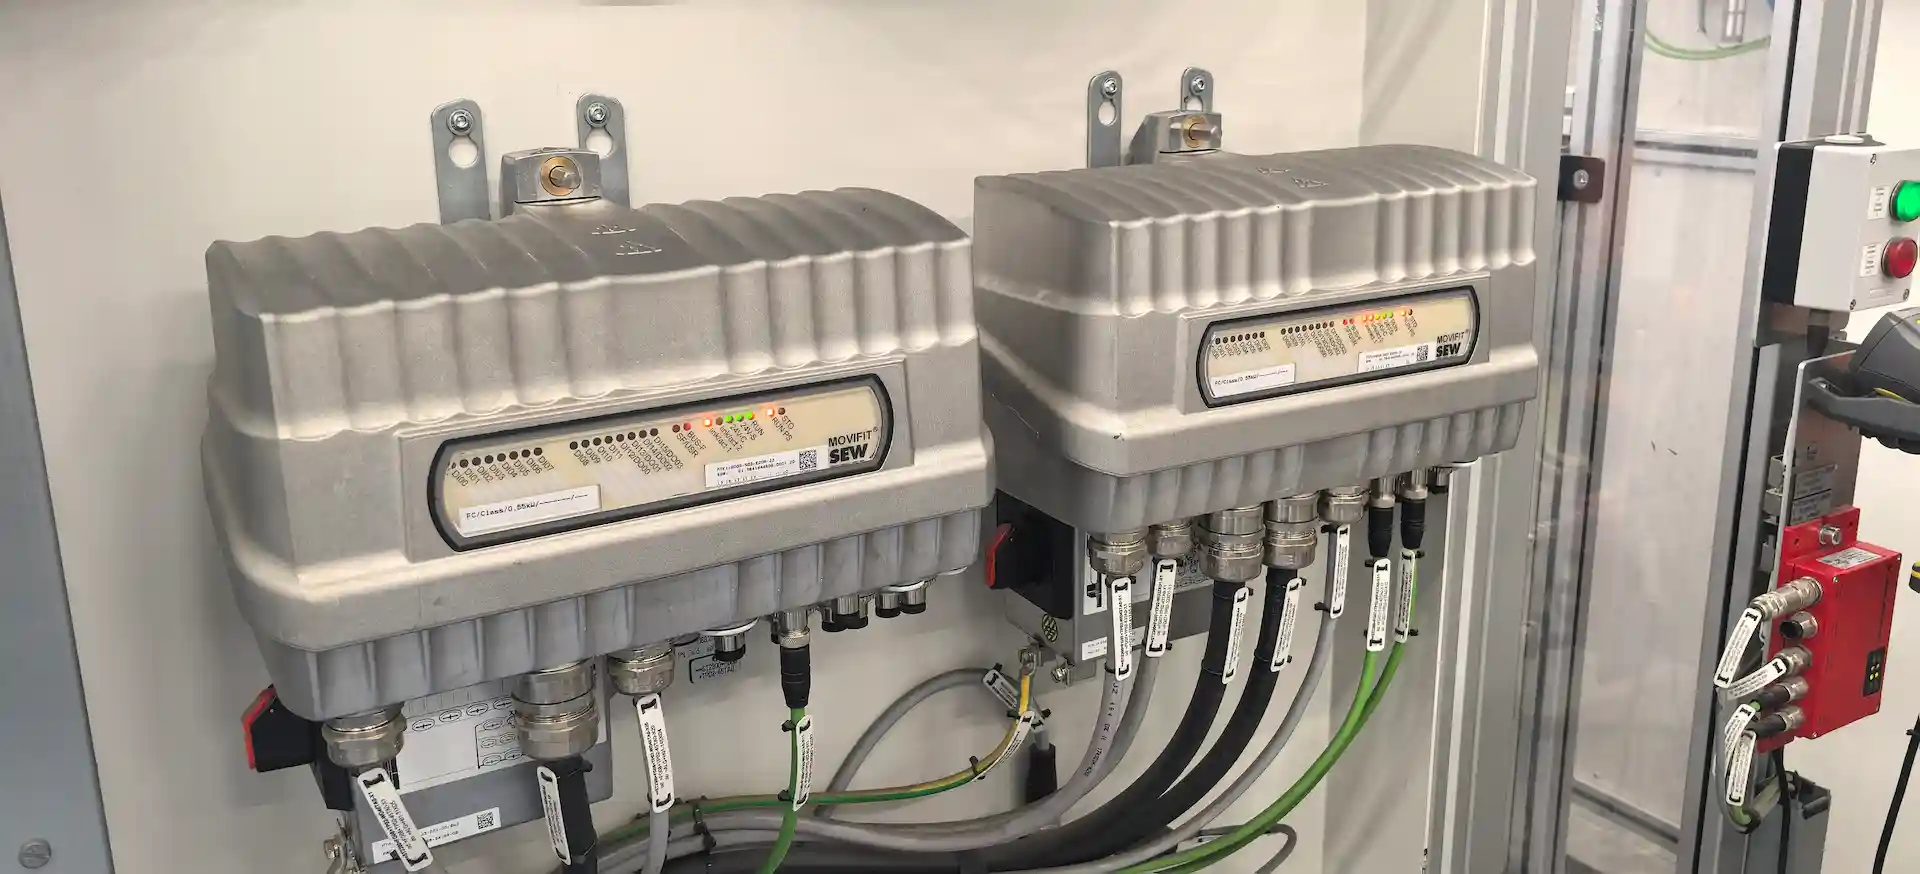
- Electrical Systems & UPS: We deployed new UPS emergency power systems to ensure data integrity and IT business continuity during power outages, alongside a complete modernization of the Poznań office electrical setup.
- Project Team: Special thanks to Marta (Legal Counsel) for GDPR regulatory structuring, Bartłomiej (IT Specialist) for technical architecture, Karol (Licensed Electrician) for electrical rewiring and compliance sign-off, and Magda and Anna for coordinating contractor DPA execution.
Result: Trusted supplier status
The outcome was not merely regulatory GDPR compliance, but achieving trusted vendor status for a client with the industry's highest security benchmarks. Designed for scalability, these same protocols now protect sensitive data across all Berlineo client accounts. This project proved that in modern technical communication, data security is an intrinsic component of translation quality.
From a personal standpoint, applying theoretical GDPR and security knowledge directly into operational engineering was deeply rewarding. Navigating these setups firsthand revealed why EU data protection directives generated such industry ripple effects. Configuring enterprise-grade backup systems professionally had an added perk: it inspired me to secure my personal files and digital family archives. And wiring electrical distribution panels was pure hands-on satisfaction.
Verified references